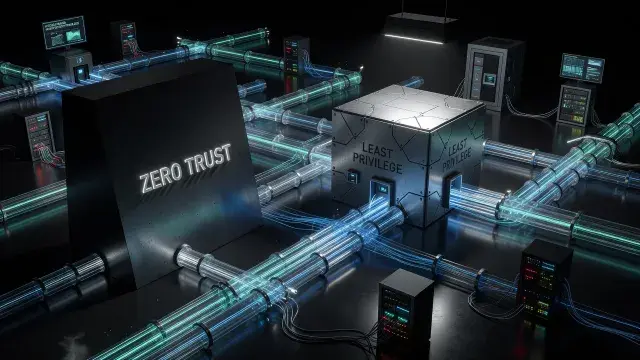
Cybersecurity teams frequently treat "zero trust" and "least privilege" as synonyms, swapping one term for the other in policy documents and vendor pitches alike. That habit obscures an important distinction. While the two concepts reinforce each other, they answer different questions about how organizations protect systems and data.
Zero trust is a security philosophy built on a simple premise: no user, device, or application should be trusted automatically, regardless of whether it sits inside or outside a network perimeter. Every request for access must be verified continuously, based on identity, device posture, location, and behavior patterns. This represents a sharp departure from older network models, which assumed that anything inside the corporate firewall was safe by default. That assumption has not held up well against modern threats, where compromised credentials and lateral movement inside networks are common attack paths. Even everyday frustrations, like troubleshooting a slow VPN connection, often trace back to the additional verification layers that zero trust architectures introduce, since constant authentication checks can add latency if not properly optimized. troubleshooting a slow VPN connection
Where Least Privilege Fits In
Least privilege, by contrast, is a narrower and older concept. It governs how much access any given user or system component should have at a particular moment, and the answer is always: the minimum necessary to perform a task, and nothing more. A finance employee does not need administrative rights to a company's entire server infrastructure. A software process reading a single database table should not have permission to modify unrelated files. Least privilege limits the damage that can result from a compromised account or a misconfigured application, because even if attackers gain entry, their reach is restricted.
How the Two Principles Work Together
Zero trust asks whether access should be granted at all, and keeps asking that question continuously, even after initial login. Least privilege determines how much access to grant once that question is answered. Together, they form a layered defense: zero trust handles ongoing verification and segmentation, while least privilege shapes the boundaries of what verified users and systems are allowed to touch. Implementing one without the other leaves gaps. A zero trust framework without least privilege might still grant excessive permissions to verified users, while least privilege without zero trust principles may rely on static, one-time access decisions that never adapt as risk conditions change.
Implications for Organizations
Adopting both frameworks requires more than new software. It demands a reassessment of identity management, network segmentation, and monitoring practices across an organization. Regulatory pressure around data protection has made this transition less optional, as auditors and compliance frameworks increasingly expect evidence of granular access controls and continuous verification. The practical payoff is a smaller attack surface and faster containment when incidents do occur, since neither trust nor access is ever assumed to be permanent.